

product
changelog
ShipShield V1 Is Live: What We Shipped (and What's Next)
ShipShield's first public release scans any AI-built app for leaked keys, missing headers, and exposed config files — free, in under a minute. Here's exactly what's live today and what's coming in Phase 2.

Hardik Desai
August 10, 2026
Latest Blogs
ShipShield V1 Is Live: What We Shipped (and What's Next)
ShipShield's first public release scans any AI-built app for leaked keys, missing headers, and exposed config files — free, in under a minute. Here's exactly what's live today and what's coming in Phase 2.
Hardik Desai
5 Things to Check Before You Share Your Lovable or Bolt App With Anyone
Before you post your AI-built app on Product Hunt, X, or Reddit, run through this five-minute checklist. Each item takes seconds to check and one prompt to fix if something's wrong.
Hardik Desai
How Non-Technical Founders Are Shipping Real Apps Without Engineers — and What It's Costing Them
AI coding tools let anyone build a working app without an engineering background. That's real progress — but it's also created a quiet security gap most builders don't know exists. Here's what the data shows.
Hardik Desai
Top 5 Security Mistakes AI-Built Apps Make
We scanned real Lovable, Bolt, Replit, and v0 apps for exposed keys, open databases, and missing headers. These five mistakes showed up again and again — and every one of them is fixable with a single copy-paste prompt.
Hardik Desai
What Is Vibe Coding, Anyway?
Vibe coding means building an app by describing it to an AI instead of writing code yourself. Here's what the term actually means, why it's exploded, and the plain-English glossary you need to understand what your AI-built app is actually doing.
Hardik Desai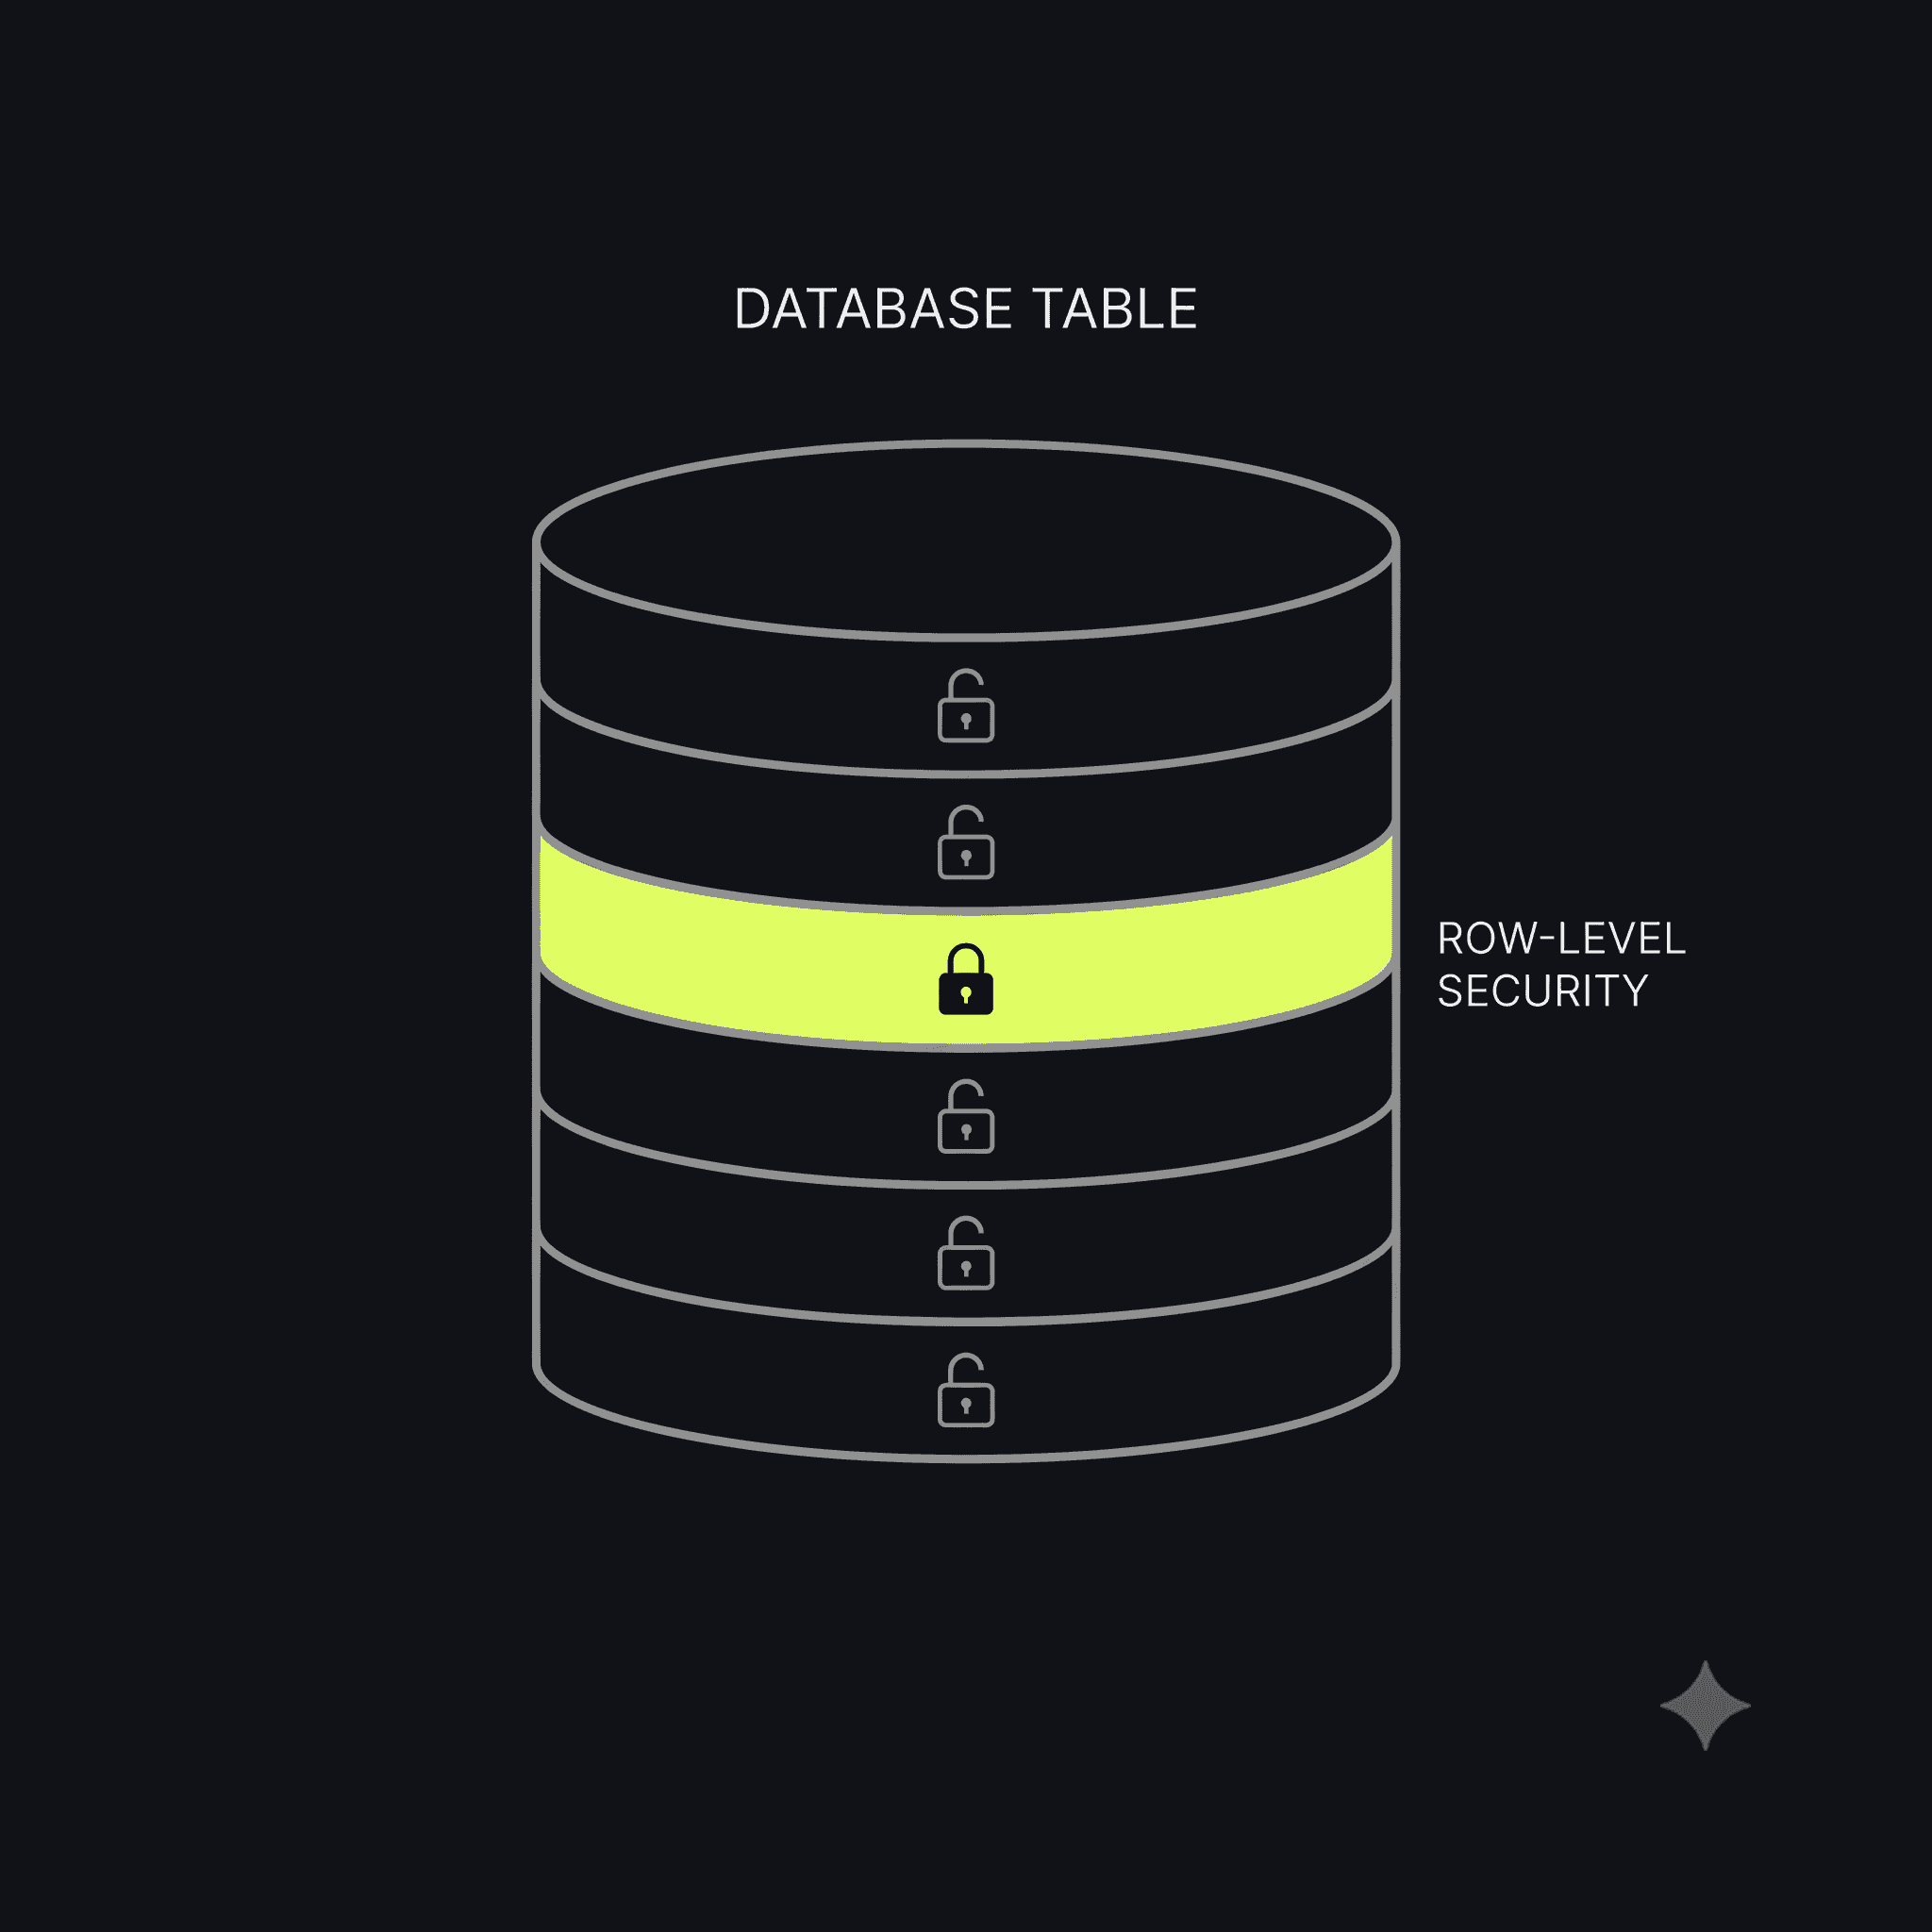
What Is Row-Level Security? The Supabase Setting That Leaves Databases Wide Open
Row-Level Security decides whether users can only see their own data — or everyone's. It's off by default on a lot of AI-generated Supabase backends, and most non-technical founders have never heard of it. Here's what it is and how to check yours.
Hardik DesaiShip Fast. Sleep Safe.
Audit your AI-built app in under 60 seconds. Catch exposed API keys and open databases before your users do.
Read-only & safe • No credentials or code modifications required